Auditing & Reporting
Centralise safety, quality, security and dangerous‑goods oversight. From reporting and audits to risk management and notifications.
Control your risks, audits and safety culture
Easily Manage
- All Audits
- Risk Management
- Management of Change
- Regulatory Reports
- Findings & RFI Register
See it in action
All your reports easily managed.
Configure company specific checklists, templates, risk matrices, tolerability levels, compliance types and report categories – so that every part of your operation stays aligned with internal and regulatory requirements.

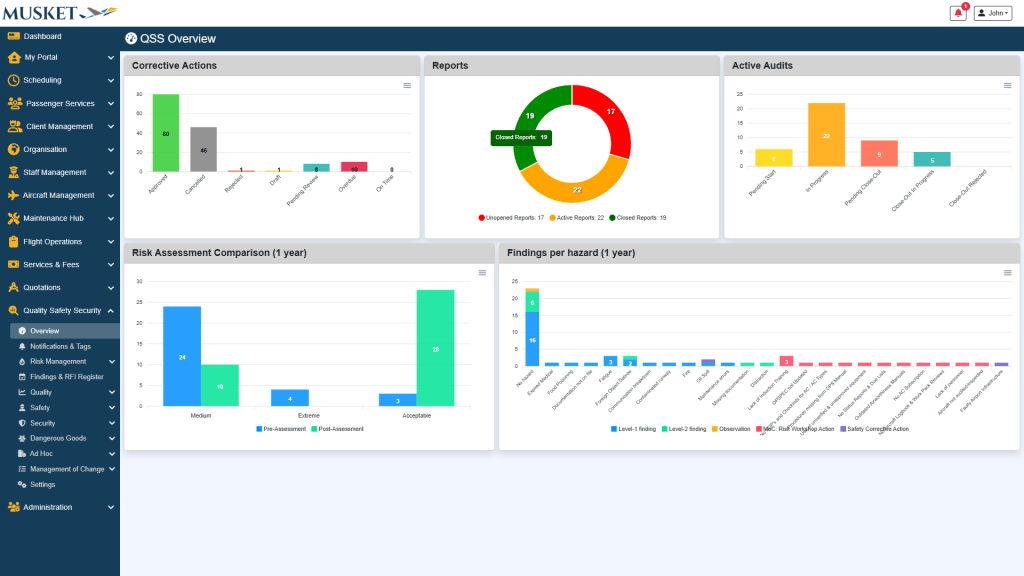
Overview
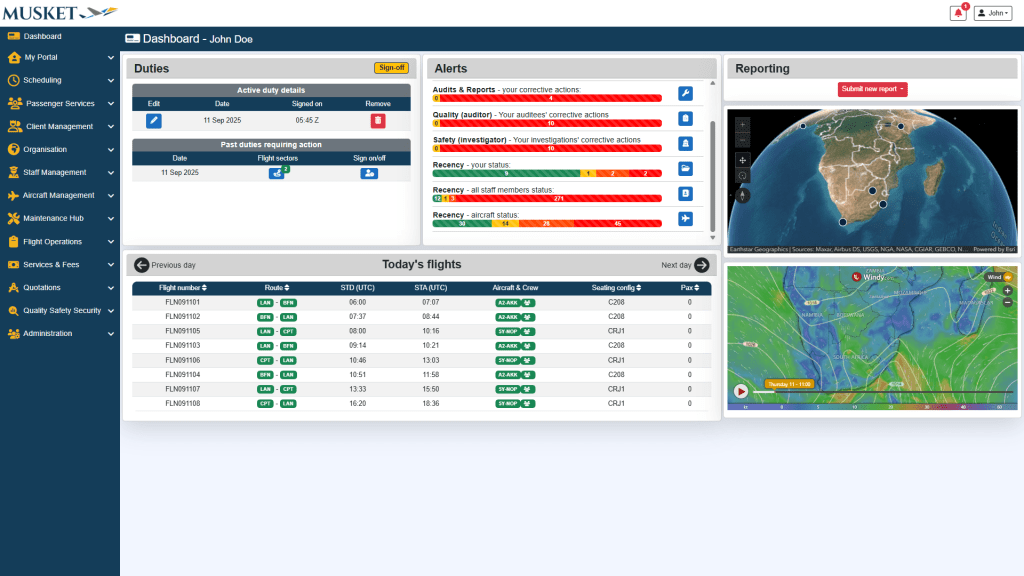
Instant situational awareness: live charts for corrective actions, reports, audits, risks, and hazards
Identify trends quickly with
pre- vs post-risk comparisons and see which hazards drive the most findings.
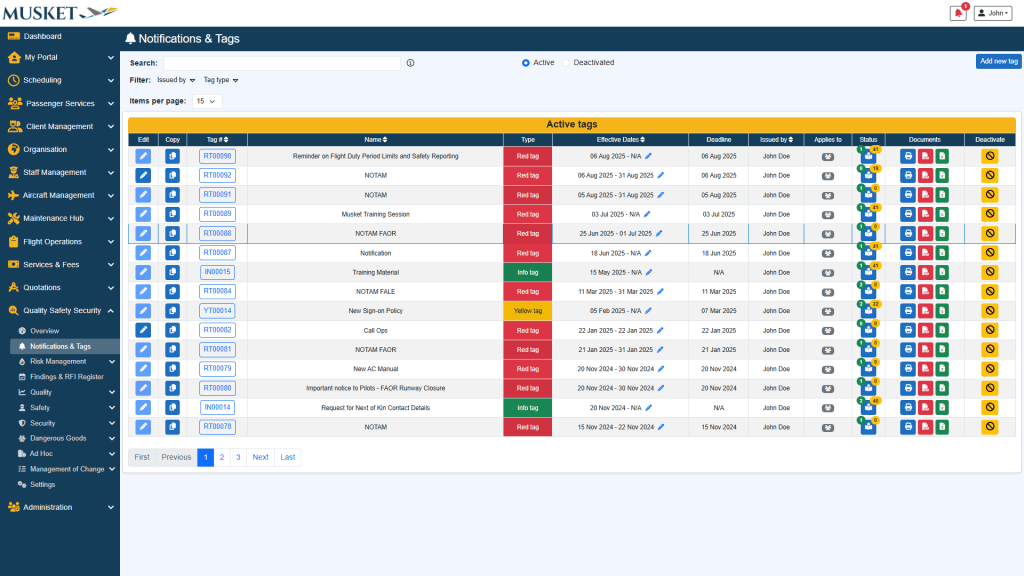
Notifications & Tags
Target and track notices with deadlines, attachments, and the exact audience you choose.
See who has acknowledged notifications, nudge stragglers by email, and keep a provable read history.
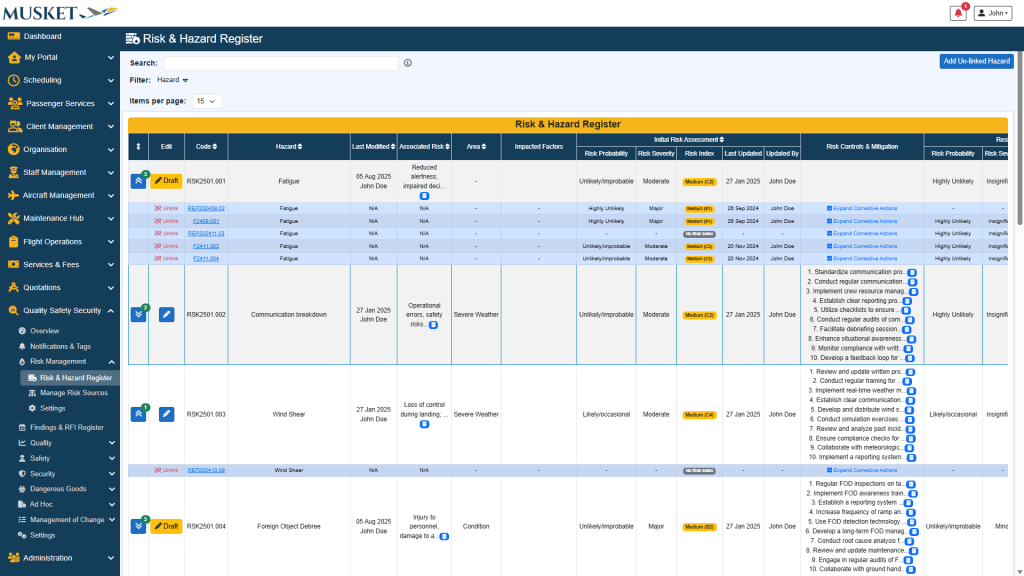
Risk
Management
One integrated register linking hazards to risks, controls, and root causes.
Define indices, impacted areas, and mitigations – or let Musket Autopilot auto-generate controls and causes to speed things up.
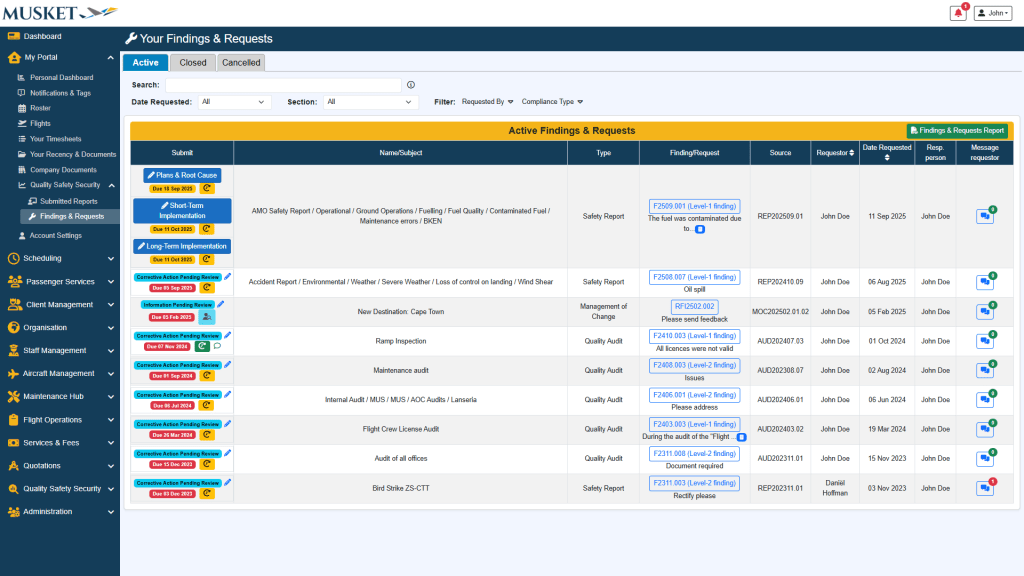
Findings & RFI Register
Treat exceptions like managed cases—from draft to close-out.
Review submissions, message owners, export reports, or add standalone actions on the fly.
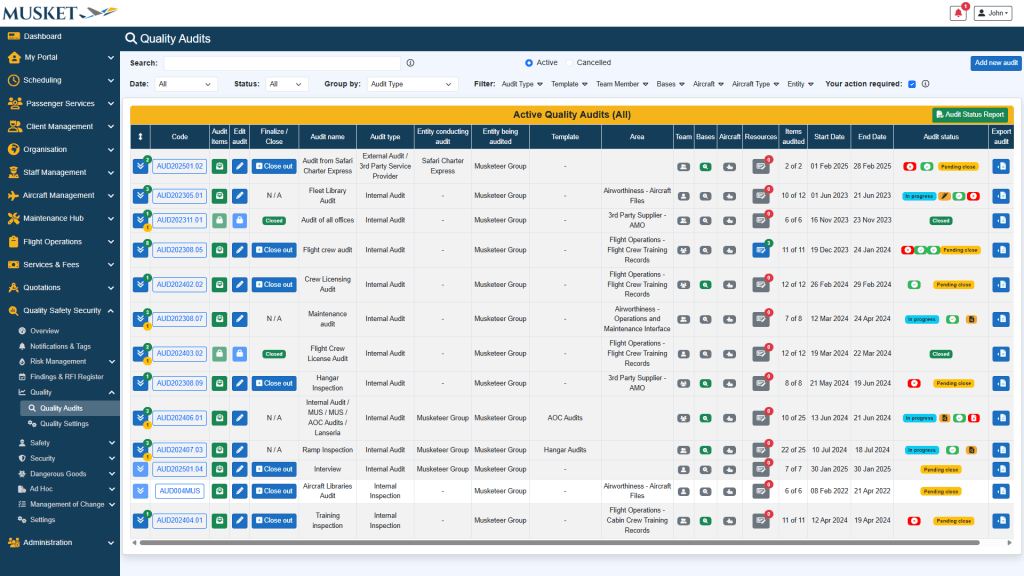
Auditing
Plan and run quality, safety, security, and DG audits with scoped checklists and linked entities.
Assign outcomes per question, raise CARs/RFIs, capture risks, and close out with executive summaries (Autopilot can help).
Reporting
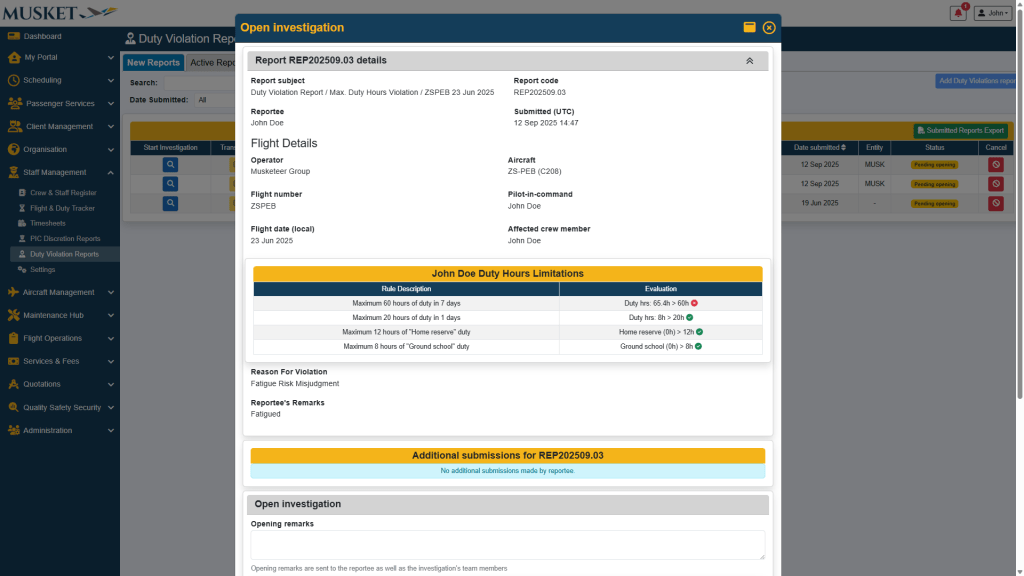
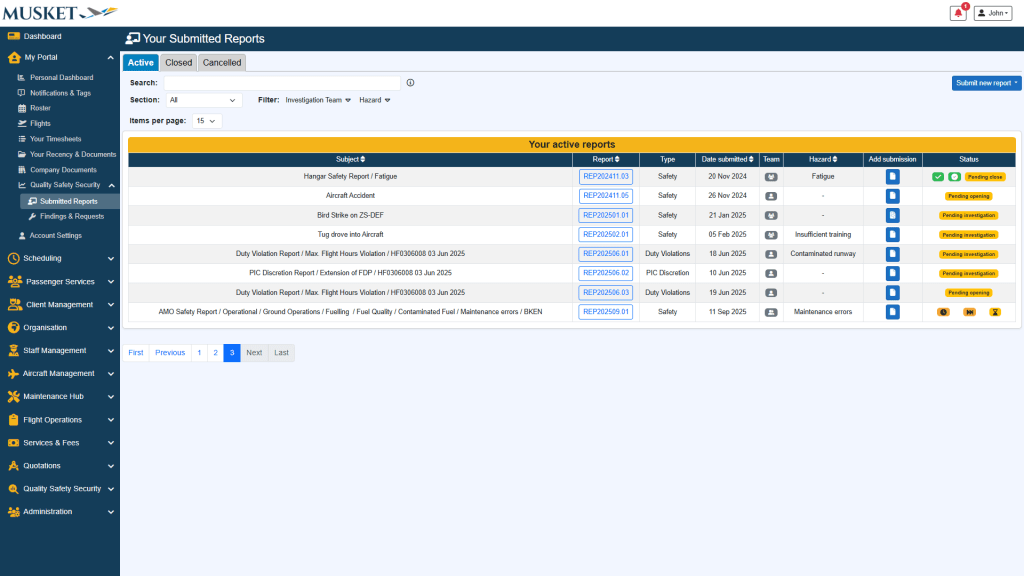
Open and investigate safety, security, dangerous-goods, and ad-hoc reports with a defined team.
Create findings, send RFIs, link hazards and pre/residual risk, and close out with a clean audit trail and alerts.
Regulatory Reports
Treat exceptions like managed cases, from draft to close-out.
Capture hazards and risks, issue findings/RFIs, request reviews, and export regulator-ready reports.
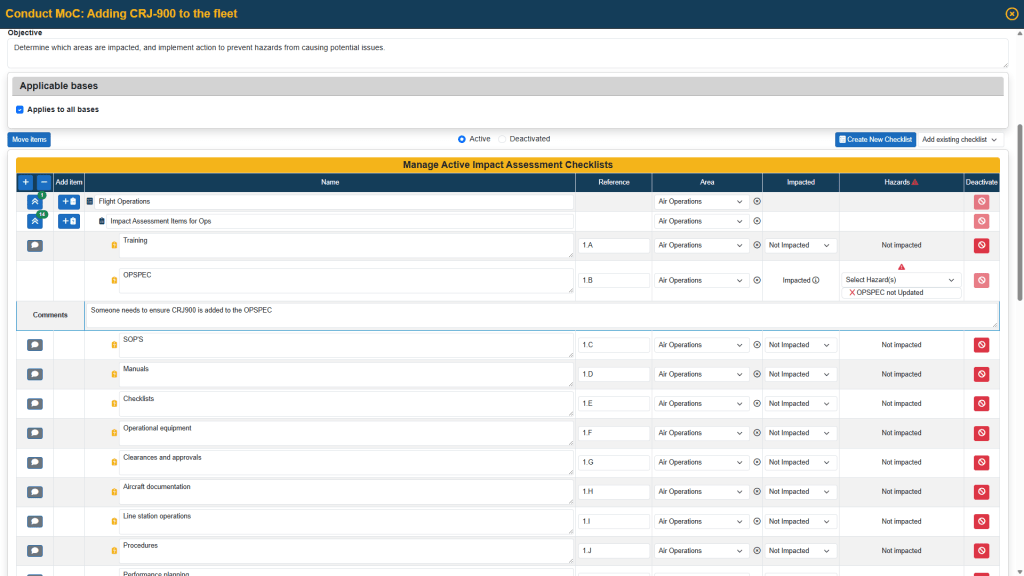
Management of Change
Run risk-based MoC assessments to see impacts before changes go live.
Assign hazards/risks and optional CARs/RFIs, then close out with team reviews and detailed reports.
Other
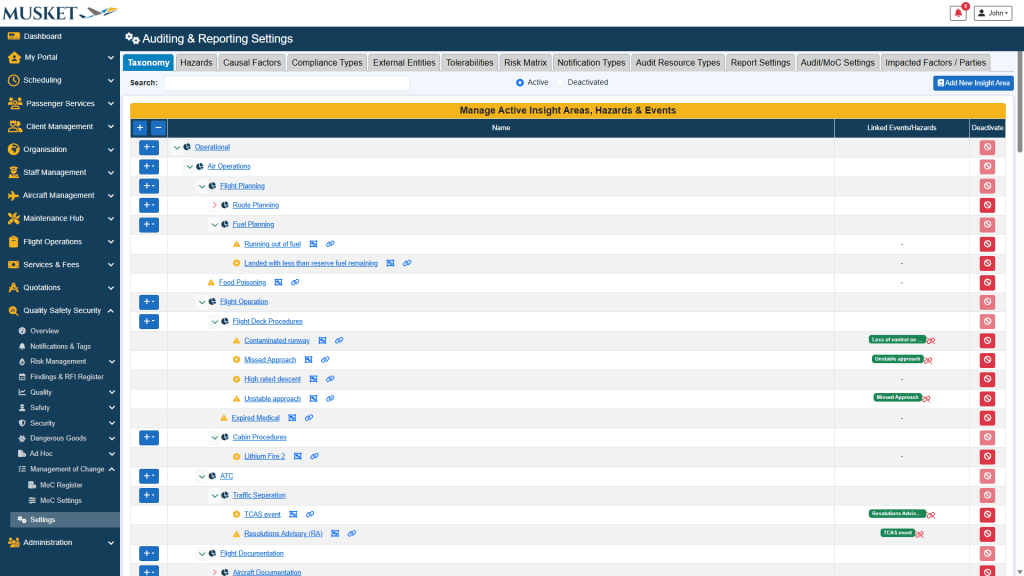
Set the rules once – risk matrices, categories, notification types (with optional sign-on restrictions), and workflow defaults.
Define taxonomies, causal factors, and external-party permissions so audits and reporting click into place across QSS.
Are looking to stay audit ready 24/7?